Docker Security - Protect Your Containers
Security Trainings
•
Simon Izydorek
•
4h
About Training
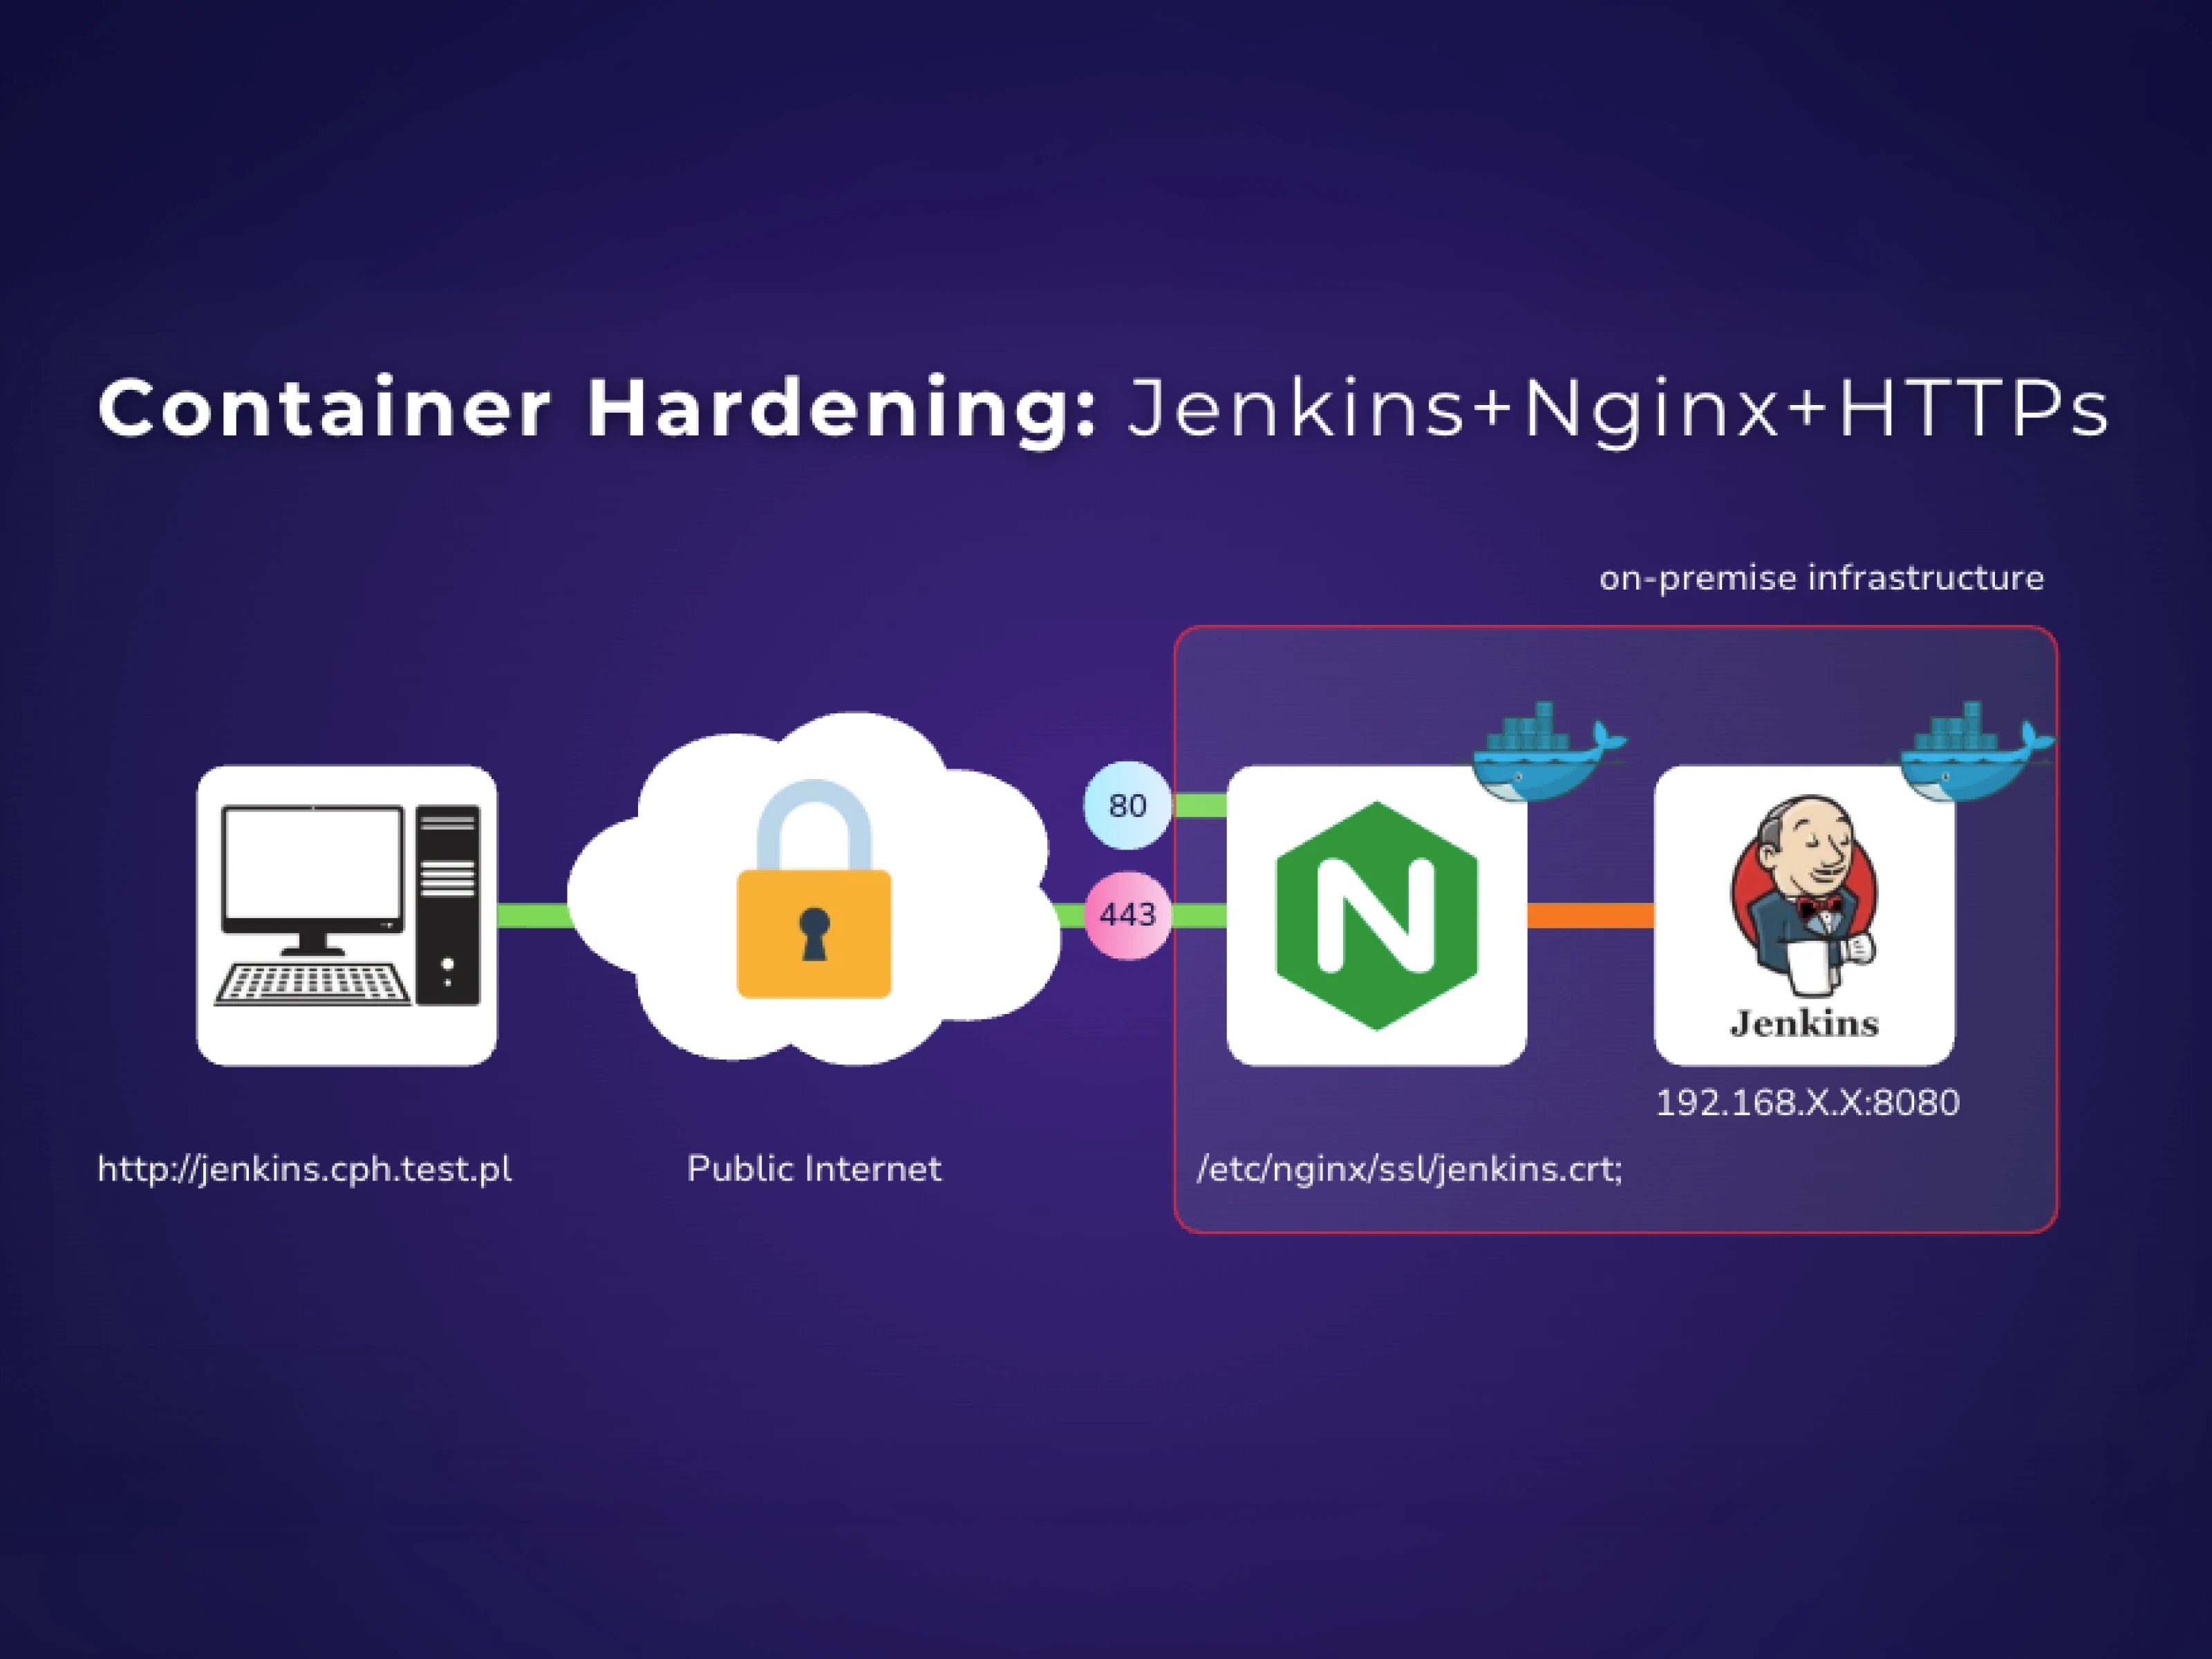
In this training, we explore Docker from a security point of view. Participants will learn about common attack scenarios, building secure images, and runtime hardening techniques through practical examples. The training is designed to combine theoretical knowledge with real-life infrastructure scenarios.
By the end of the session, attendees will have hands-on experience applying security practices in real Docker deployments, supported by a practical security checklist for everyday development.
Exemplary content of the training in the next slides.
Training Overview
Basics of Security in Containers
Why a container ≠ full isolation
Most common attack scenarios on containers
Secure Images
Choosing base images (official vs. custom)
Most common mistakes in Dockerfile and their
consequences
Runtime Hardening
Mechanisms --cap-drop and --cap-add (practical
examples)Read-only filesystem and mount restrictions
Design of a sample “hardened” container
Private registries
As a professional cybersecurity unit, our standards for security training are high. Szymon met these expectations by delivering a session that stripped away the basics to focus entirely on advanced exploitation vectors and defense strategies.
Maksym Brzęczek - Cybersecurity Engineer, Board Member@Efigo

Category
Security Trainings
Duration
4h workshop
Trainer

Simon Izydorek
Specialization: Ansible, Docker, Kubernetes, DevSecOps, Linux, Falco.
Experience: Over 10 years in IT. Designed, implemented, and maintained infrastructure for global leaders such as Nokia, Tieto, and Thales. Regular speaker at prestigious industry conferences (DevOpsDays Aarhus, DevOpsDays Geneva, Linux Session, SO/DO Poland).